Collect, understand and act on your security data.
Oriana is a Security Data Platform that covers SIEM capabilities but goes beyond the SIEM category. The patented Minimize algorithm delivers predictable performance at any scale, lower resource consumption and a lower total cost of ownership.
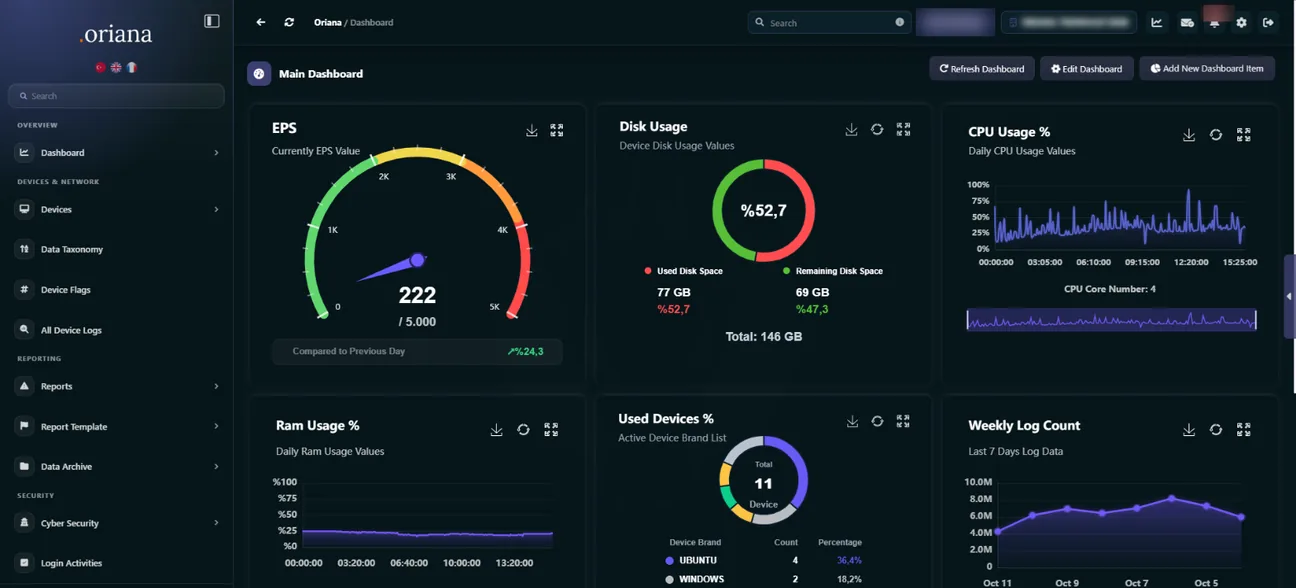
Try OrianaSIEM right now, with nothing to install.
The real product interface, running on a sample organization's data. Walk through every screen yourself: from the dashboard to triggered correlations, from raw logs to MITRE ATT&CK mapping.
- No form, no account: one click takes you into the product interface
- A 10-step guided tour shows how Oriana works in 5 minutes
- 14 sample devices, correlations picked from the 3,500+ rule library, a live alert stream
Start the Live Demo
You have the logs. But can you actually use them?
Most organizations collect logs; yet fragmented architecture, high licensing and hardware costs, dependence on specialists and audit pressure keep that data from turning into value. Oriana does not just collect logs; it understands them and turns them into action.
Our platform approachThe cost of the traditional approach
- Licenses that grow with data volume; log sources left unconnected because of cost
- High CPU, RAM and disk requirements for Elasticsearch/JVM-based engines
- Proprietary query languages and consultant dependency; projects that take 6-12 months
- Data residency and data egress cost risk in cloud SIEM
- Person-days lost to audits; manual report preparation
With Oriana
- Connecting a source does not grow your license; every log reaches the platform
- Low resource consumption with a proprietary, non-Elasticsearch data engine and microservice architecture
- Installed in 1 day once the server is ready; measured POC results in 1-2 weeks
- Data sovereignty: on-premise, hybrid or in a partner cloud
- Ready-made reporting support for GDPR, ISO 27001, PCI DSS, Turkish Law 5651 and KVKK
One platform, two products. The full lifecycle of security data.
From log collection to time-stamped archive, from correlation to threat intelligence; both products share the same architecture and the same interface language.
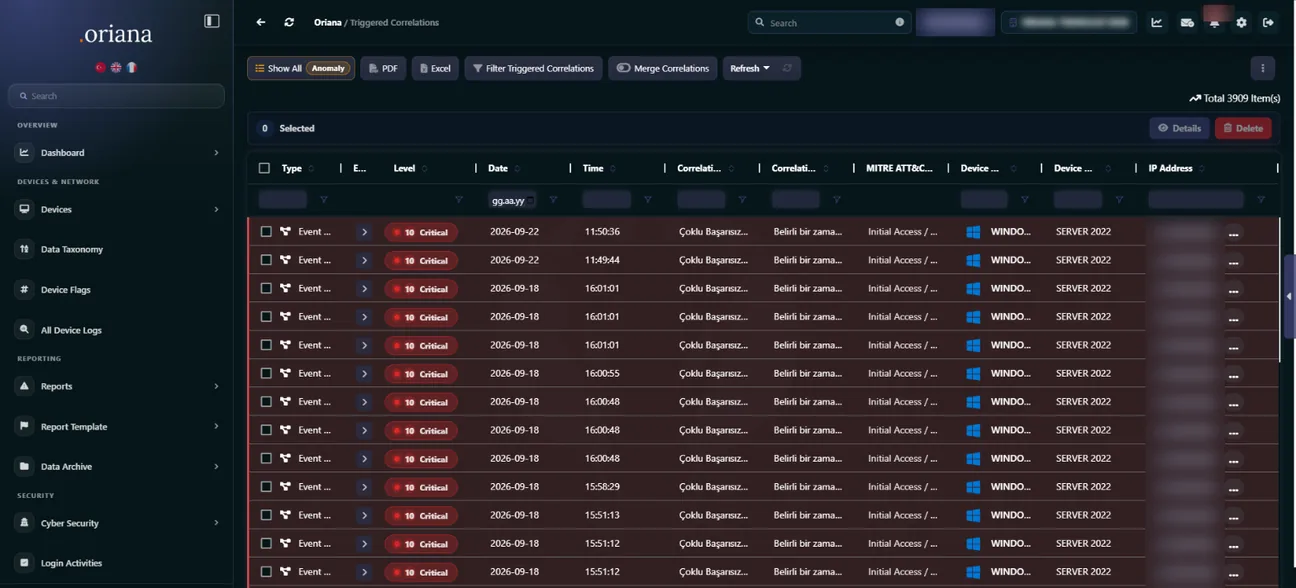
A SIEM platform that collects security events from diverse sources, analyzes them with 6 correlation engines and UEBA, and maps them to MITRE ATT&CK.
- 3,500+ ready-made rules, Sigma & YARA support
- Profiling-based UEBA (no extra license)
- USOM & CTI threat intelligence
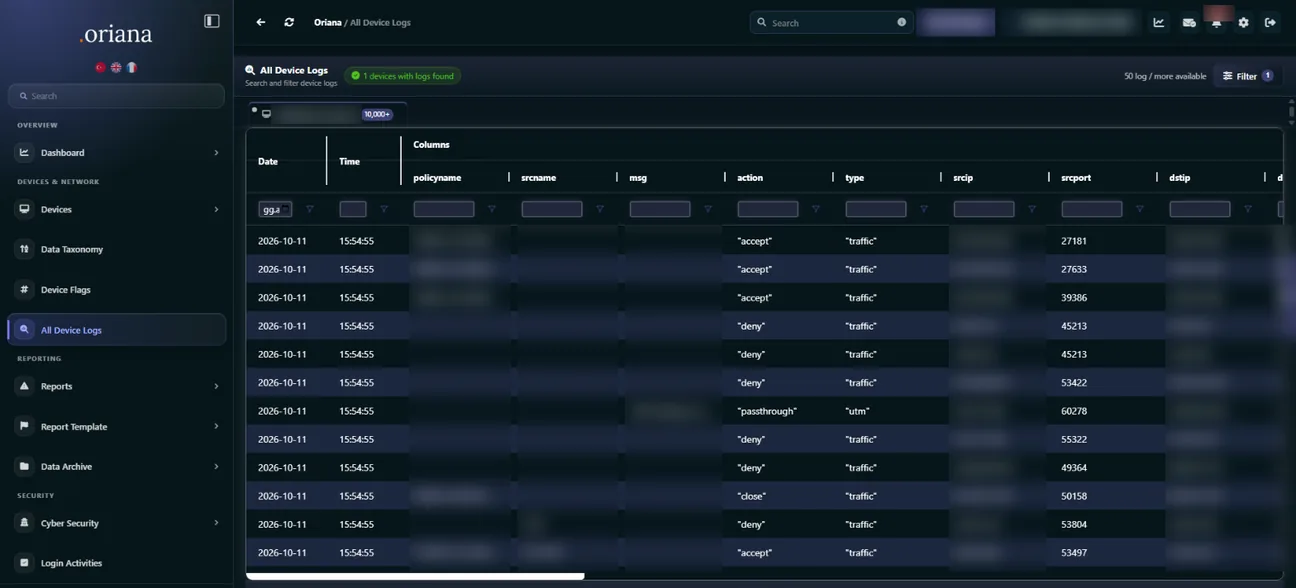
Not a feature. A patented security data architecture.
The patented Minimize algorithm searches live data without going to the archive; Deduplication strips out repeated records. The result: predictable performance at any scale and a lower total cost of ownership.
- Log management, SIEM, archive and correlation in a single architecture
- Microservice design; horizontal scaling, zero-downtime updates
- Data sovereignty: on-premise, hybrid, cloud or appliance
- Less CPU, RAM and disk
Table view
| Resource | Elasticsearch-based | Oriana |
|---|---|---|
| CPU | 100 | 25 |
| Memory | 100 | 50 |
| Disk | 100 | 30 |
Query response time of 0.95 ms in internal tests. Values depend on specific test scenarios; contact us for a comparative POC on your own data.
Detection starts on the day it is installed.
Point your log sources at the platform without changing your existing infrastructure; the platform handles the rest.
Collect
Ingest logs from firewalls, AD, DNS, servers, databases, antivirus, DLP, network devices and applications via Syslog, Agent, NetFlow/sFlow, SFTP/SMB/FTP and API. Automatic device discovery identifies sources in seconds.
Understand
Logs are parsed, normalized and tagged with a severity level from 1 to 10; then enriched with GeoIP, threat intelligence and asset context. AI-assisted parsing brings new sources online quickly.
Detect
3,500+ ready-made rules, Sigma and YARA support, time/counter/event-chain/time-delta correlations and UEBA profiling turn threats into alarms mapped to MITRE ATT&CK tactics.
Act & Report
Respond instantly with e-mail, SMS and automated SSH actions. Generate scheduled or on-demand reports; archive logs with a legally valid time stamp and stay audit-ready.
Built for heavily regulated organizations with high data volumes.
From public institutions to banks, from hospitals to retail chains; more than 700 organizations manage their security data with Oriana.
Industry solutionsEnterprises
Simplifies IT operations by centralizing logs from disparate systems; brings security, audit and regulatory processes under control.
Public Sector & Critical Infrastructure
Secures audit processes with log collection and time-stamped retention that meet Turkish Law 5651, e-signature law 5070 and KVKK requirements; keeps data inside the organization.
MSSPs
Monitor all customers from a single console with multi-tenancy; isolated data, rules and reports per tenant. Shared-server costs split across customers.
ISP / CSP Partners
Offer log management and security services to your customers as a value-added service; manage hundreds of customers on a scalable architecture.
Whichever jurisdiction audits you, your report is ready.
Reporting and traceability support for international and national regulations.
You decide where your data lives.
On-Premise
All data stays in your own infrastructure. Runs on physical or virtual (VMware, Proxmox, KVM) servers, fully aligned with internal systems.
On-Cloud
Fast start with no infrastructure investment. Flexible scaling on demand; capacity grows automatically under load.
Appliance
Hardware and software together, pre-installed and optimized as a plug-and-play solution. Minimal setup time, stable performance.
MSSP / Multi-Tenant
Shared server in the partner's cloud or in Oriana's cloud; isolated data per customer. New customers onboarded within hours.
Voices from the field
“We can now detect attacks early and meet the SIEM, log and SPOT requirements of payment-systems regulations with a single technology.”
“We consolidated all logs from different systems on a single platform. Our audit and analysis processes became significantly faster.”
Latest updates
OrianaSIEM receives A-Level Conformity Certificate in TRTEST SIEM testing
Fully meeting the TRTEST criteria, OrianaSIEM offers organizations a validated security solution with high-performance correlation and advanced analytics infrastructure.
TRTEST certification detailsOrianaSIEM V1.0: more than 330 new features and improvements
Event Chain and TimeDelta correlations, Sigma/YARA and MITRE ATT&CK support, UEBA, USOM integration and hardened security; together with the Web API and a new user interface.
What's new in OrianaSIEM V1.0Oriana gains momentum in the global market
Building on its success in EMEA, Oriana is opening up to international organizations with German and French interfaces and GDPR/NIS2/DORA compliance.
Oriana's global growthInstalled in 1 day. Measured POC results in 1-2 weeks.
Let's measure query time, resource consumption, deduplication ratio and MTTD/MTTR scenarios together, on your own log sources.