.OrianaLOG
Central log management: bring all your logs into one place.
Centrally collects all logs from Active Directory, DNS, Office 365, firewalls, servers and network devices, archives them with a legally valid time stamp and makes millions of records accessible within seconds. SIEM-style "one-shot correlation" raises an instant alarm on critical events.
* Values measured in specific internal test scenarios.
Don't just store logs. Manage them, analyze them, present evidence.
Central Log Collection
Gain visibility and ease of management by collecting logs from all systems in one place. Add sources in seconds with automatic device discovery.
Long-Term Secure Retention
Archive log records while preserving data integrity. Collected data is stamped daily with a TÜBİTAK-approved time stamp under Turkish e-signature law 5070.
Fast Search and Access
With the patented Minimize algorithm, reach records from years ago within minutes, on live data, without pulling anything from the archive.
Regulatory Compliance
Log retention and record management infrastructure that meets requirements such as GDPR, NIS2, ISO 27001, PCI DSS, Turkish Laws 5651 and 5070, and KVKK.
No indexing database. 0.95 ms queries regardless of data age.
OrianaLOG and OrianaSIEM share the same patented core. Logs are not written to an indexing database such as Elasticsearch; historical queries are answered on live data, without going to the archive, no matter how old the record is. With no indexing, resource consumption stays low as well.
The patented algorithm lets you search live data without pulling from the archive; a 1-day-old or 2-year-old record returns at the same speed. No Elasticsearch or JVM-based index layer is required.
Get rid of the clutter of redundant, constantly repeating records. A compiled, duplicate-free structure reduces storage usage on your system by up to 70%.
Tag incoming events according to your needs and gain meaningful insight on subsequent occurrences of the same log type. Our team provides tagging support for ready-made tags.
Table view
| Month | Raw logs (units) | Oriana (units) |
|---|---|---|
| 1 | 100 | 30 |
| 6 | 600 | 180 |
| 12 | 1,200 | 360 |
The deduplication ratio depends on the test data set; 70% is the upper value measured in an internal test scenario. Memory 50% and CPU 75% lower; query response time 0.95 ms.
Without an indexing database, an in-memory structure and file-archive approach keep it optimized under high EPS; there is no Elasticsearch or Kibana dependency. Runs on a single server or container and scales with a cluster architecture when needed. Values measured in internal test scenarios.
The correlation you need, without the cost of a SIEM.
Many organizations pay a high price for a SIEM even though they never use cross-source or time-based correlation. OrianaLOG's one-shot correlation engine raises an alert the moment an event is detected in a log; it informs the user immediately and enables a response.
OrianaLOG offers SIEM-like correlation, but because it performs single-rule correlation it is not a full SIEM. For event chains, UEBA and threat hunting, moving to OrianaSIEM is always possible; the two products share the same architecture.
Some of the events one-shot correlation can detect
- Failed login and VPN attempts
- Unauthorized access attempts on administrator accounts
- Unauthorized file sharing; file deletion, copying, creation
- Data encryption attempts and data leakage detection
- Suspicious network traffic and DDoS attack detection
- Unauthorized software installation attempts
- Malware infection events
- Unexpected outages of critical services
- Backup job failures
- Access to databases and highly sensitive data
- Critical system changes and application errors
- Insider threats and abnormal user activity
With or without an agent; from every source.
Logs are collected agentlessly over Syslog (UDP/TCP/TLS), NetFlow/sFlow, API, SFTP/SMB/FTP file sources and database connections. The agent is optional; where needed, OrianaAJAN collects Windows, file audit and application logs.
Active Directory
- Successful / failed login attempts
- User creation / deletion
- Permission and Group Policy changes
DNS
- Domain queries, suspicious DNS requests
- DGA / abnormal traffic
- Internal / external DNS activity
Office 365
- User sign-in activity, MFA / failed logins
- Mail sending / access logs
- Admin operations
Firewall
- Allowed / blocked traffic, port access
- VPN connections
- Threat / IPS logs
Network (Switch / AP)
- Connected devices, MAC / IP mappings
- Port activity
- Network access events
Servers and Applications
- Windows / Linux logs
- IIS / Apache / Nginx web server logs
- Application logs (text, JSON, XML, CSV)
SQL / Databases
- Database access records, ODBC/JDBC
- Successful / failed queries
- Authorization and role changes
Antivirus / EDR
- Detected malware
- Quarantine and deletion actions
- Update and signature status
DLP & Others
- Sensitive data access and leakage attempts
- USB / e-mail / export activity
- IoT, storage, fingerprint systems, SNMP traps, PCAP
Monitor file and folder access in real time.
File Audit is a critical security component that tracks file and folder access, changes and permission assignments on your systems in detail. OrianaLOG does more than collect logs; it analyzes file events in real time, detects improper activity and raises alarms.
| Event Type | Description | Example |
|---|---|---|
| Create | Logged when a new file is created | cost.xlsx was created by "omer.tan" |
| Delete | Detected when a file or folder is deleted | employee-records.docx was deleted by "ahmet.kara" |
| Rename | A file or folder name is changed | annual_plan.docx → 2025_annual_plan.docx |
| Read | A file is viewed | User opened finance2024.pdf at 23:54 |
| Write / Modify | File contents are changed | New data was added to CRM_CustomerList.xlsx |
| Copy | A file is copied to another location | patent.pdf was copied to a USB drive |
| Permission Change | A permission is added to or removed from a file | "everyone" was granted access to staff_confidential.txt |
Up and running in three steps.
Forward your logs
Point your devices' event logs at OrianaLOG via Syslog, NetFlow, API, file source or agent; automatic device discovery recognizes the sources.
Configure your settings
Define device-specific tags, filter shortcuts and one-shot correlation rules; choose your reporting and archive policies.
Monitor your systems with ease
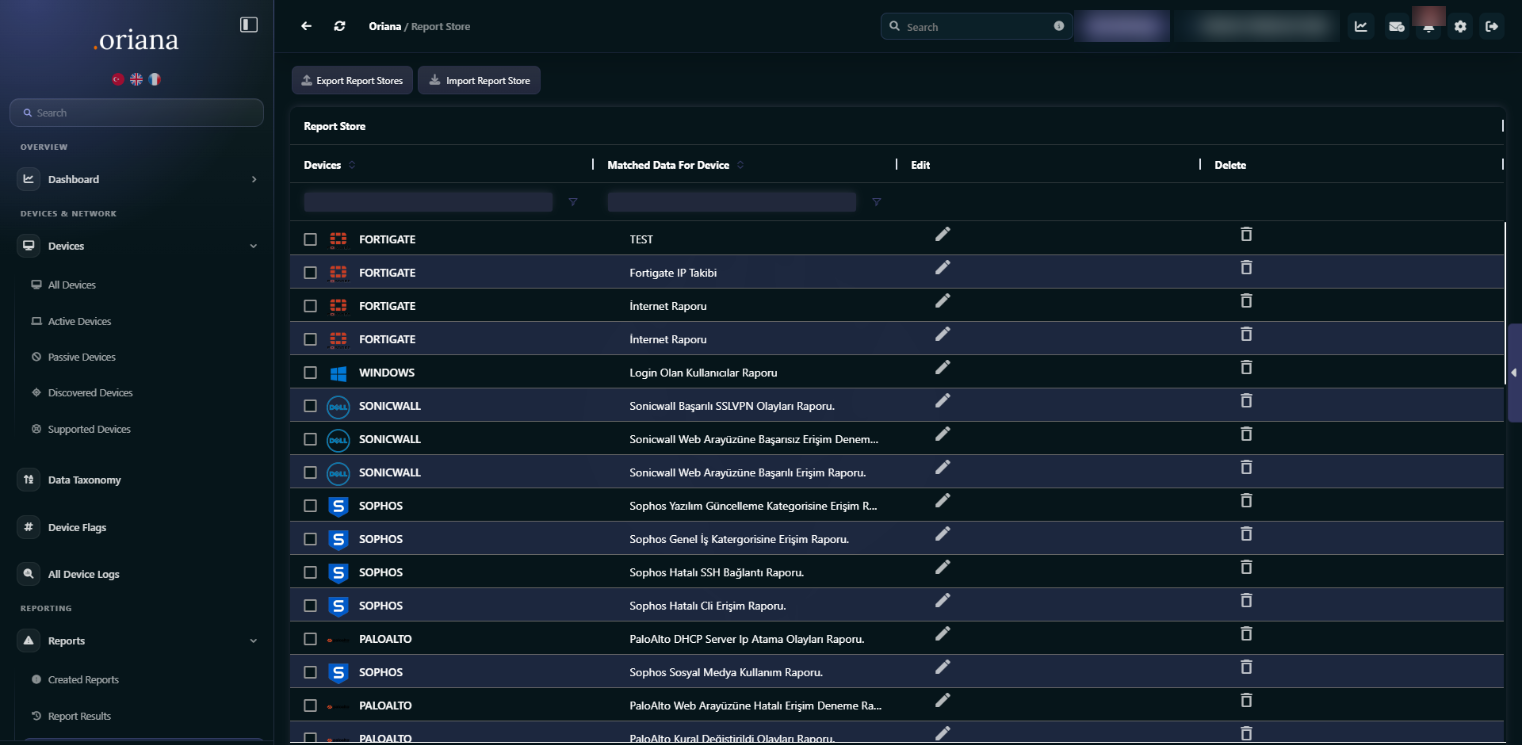
Track your environment with dashboards, reports and filters. Get on-demand, daily, weekly and monthly reports as PDF/Excel or distribute them by e-mail.
Put an end to scattered logs.
Manage all your data on a single platform; present evidence within minutes during audits.