.OrianaSIEM
Next-generation SIEM solution: see threats, respond instantly.
A next-generation SIEM that centralizes security events from servers, firewalls, switches, access points, antivirus, DLP and similar systems, then evaluates them with correlation rules, behavior analysis and threat intelligence to make potential threats visible. Self-hosted with full data sovereignty: on-premises, hybrid or private cloud.
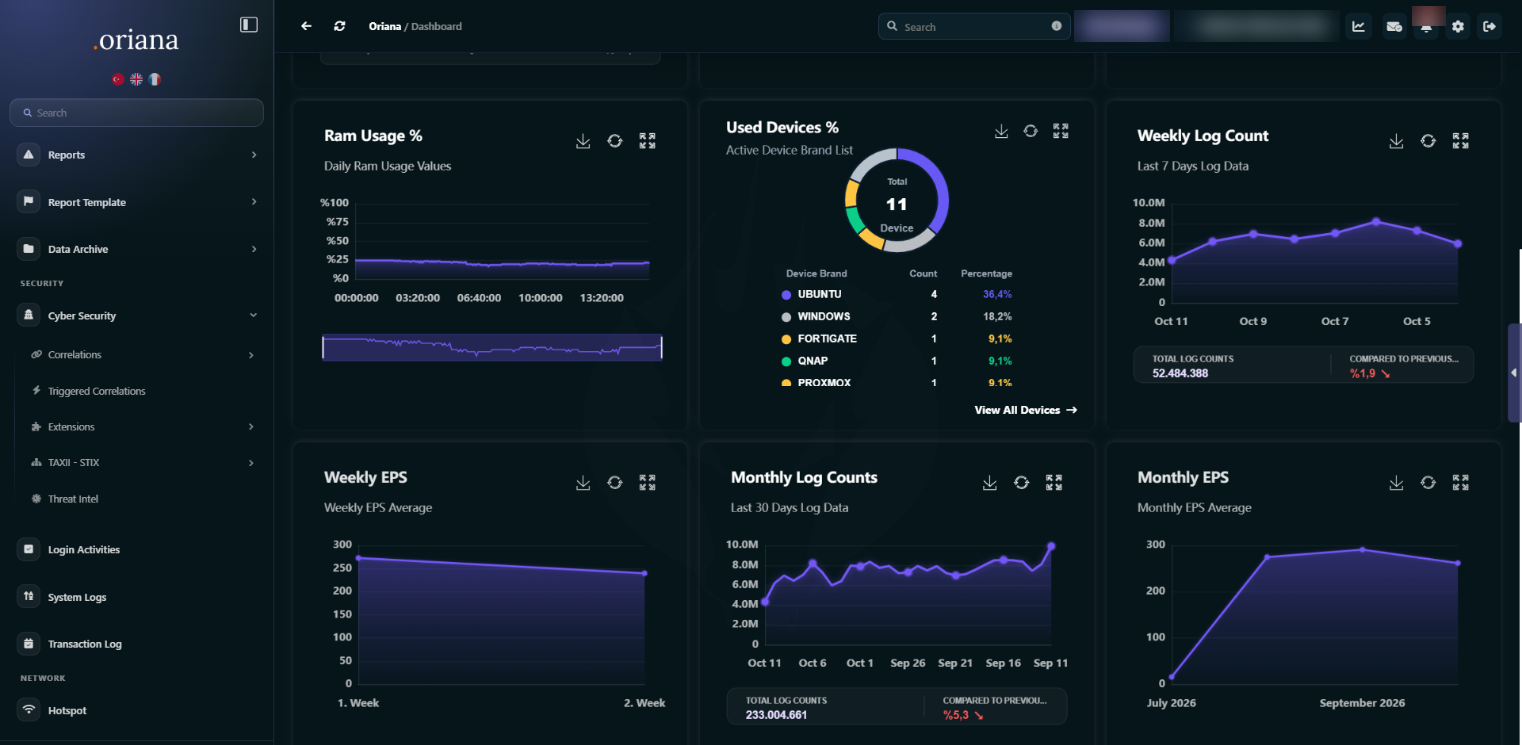
Try OrianaSIEM right now, with nothing to install.
The real product interface, running on a sample organization's data. Walk through every screen yourself: from the dashboard to triggered correlations, from raw logs to MITRE ATT&CK mapping.
- No form, no account: one click takes you into the product interface
- A 10-step guided tour shows how Oriana works in 5 minutes
- 14 sample devices, correlations picked from the 3,500+ rule library, a live alert stream
 Start the Live Demo
Data sovereignty. Predictable TCO. In-house R&D, fast time to value.
A TRTEST A-Level (Türkiye) certified SIEM platform, engineered by Oriana, that keeps data inside the organization and is deployed at international scale.
Data Sovereignty & Regulation
Logs stay under the organization's control. Reporting and traceability support for GDPR, NIS2, ISO 27001, PCI DSS, Turkish Law 5651 and KVKK audits.
Predictable Total Cost
No volume-based license growth and no cloud data egress fees. Low dependence on specialists; license, hardware and operating costs fall together.
Manufacturer-Direct Support
Requests go straight to the product team. Installed in 1 day once the server is ready, measured POC results in 1-2 weeks, live within days.
No indexing database. 0.95 ms queries regardless of data age.
The shared core of OrianaSIEM and OrianaLOG is the patented Minimize algorithm. Logs are not written to an indexing database such as Elasticsearch; historical queries are answered on live data, without going to the archive, no matter how old the record is.
- No Elasticsearch or JVM-based index layer required
- Time-independent queries: a 1-day-old or 2-year-old record, same speed
- Low CPU, RAM and disk consumption because nothing is indexed
- Deduplication strips out repeated records and shrinks storage
Table view
| Data age | Index-based (relative) | Oriana |
|---|---|---|
| 1 day | 1.0 | 0.95 ms |
| 1 month | ~2 | 0.95 ms |
| 1 year | ~5 | 0.95 ms |
| 2 years | ~8 | 0.95 ms |
The Oriana value was measured in internal test scenarios; the index-based curve is illustrative of typical behavior and is not a measurement of any specific product. Contact us for a comparative POC on your own data.
See attack behavior, not isolated log records.
OrianaSIEM analyzes security events from diverse sources with six advanced correlation engines and turns them into meaningful alarms. Recurring events and chained threat scenarios become visible.
Detection starts on the day it is installed. More than 3,500 ready-made correlation rules and the Sigma catalog provide coverage from day one; there is no proprietary query language such as KQL/SPL to learn.
One Shot (Rule-Based)
- Instant analysis of single events against content, filter or pattern rules
- Fast alarm generation, low resource consumption
Time-Based & Counter-Based
- Threshold breaches within a defined time window (e.g. 10 failed logins in 5 minutes)
- Cumulative counters and statistical deviation detection
Event Chain
- Links related events using attack-chain logic
- Tree and path views; multi-device and cross-source correlation
Time-Delta
- Analyzes the time difference between two events
- V2: learning period, profile- and anomaly-based detection
Sigma & YARA Detection
- Log-based threats with Sigma rules; YAML import and repository sync
- File- and content-focused indicators with YARA (e.g. suspicious PowerShell)
Script & Exception-Based
- Script-based custom correlation (built-in code editor)
- "Missing event" detection: alarm when an expected backup does not run
Profile behavior without naming a single user.
OrianaSIEM has an advanced behavior-analysis infrastructure that analyzes the behavior of users, devices, IP addresses, applications, sessions and other entities found in logs. When building a correlation you do not define a specific user or IP; you choose which field to profile and the system builds a dynamic behavior profile for every entity.
- Activity outside working hours
- Access from different locations within a short time
- Unusual application execution
- Access to systems not normally used
- Devices generating abnormal traffic
- Suspicious session and process chains
Profilable fields are unlimited: user, source_ip, destination_ip, mac_address, hostname, process_name, application, session_id, browser, domain and any other field in the log.
Not an alarm; threat data tied to attacker behavior.
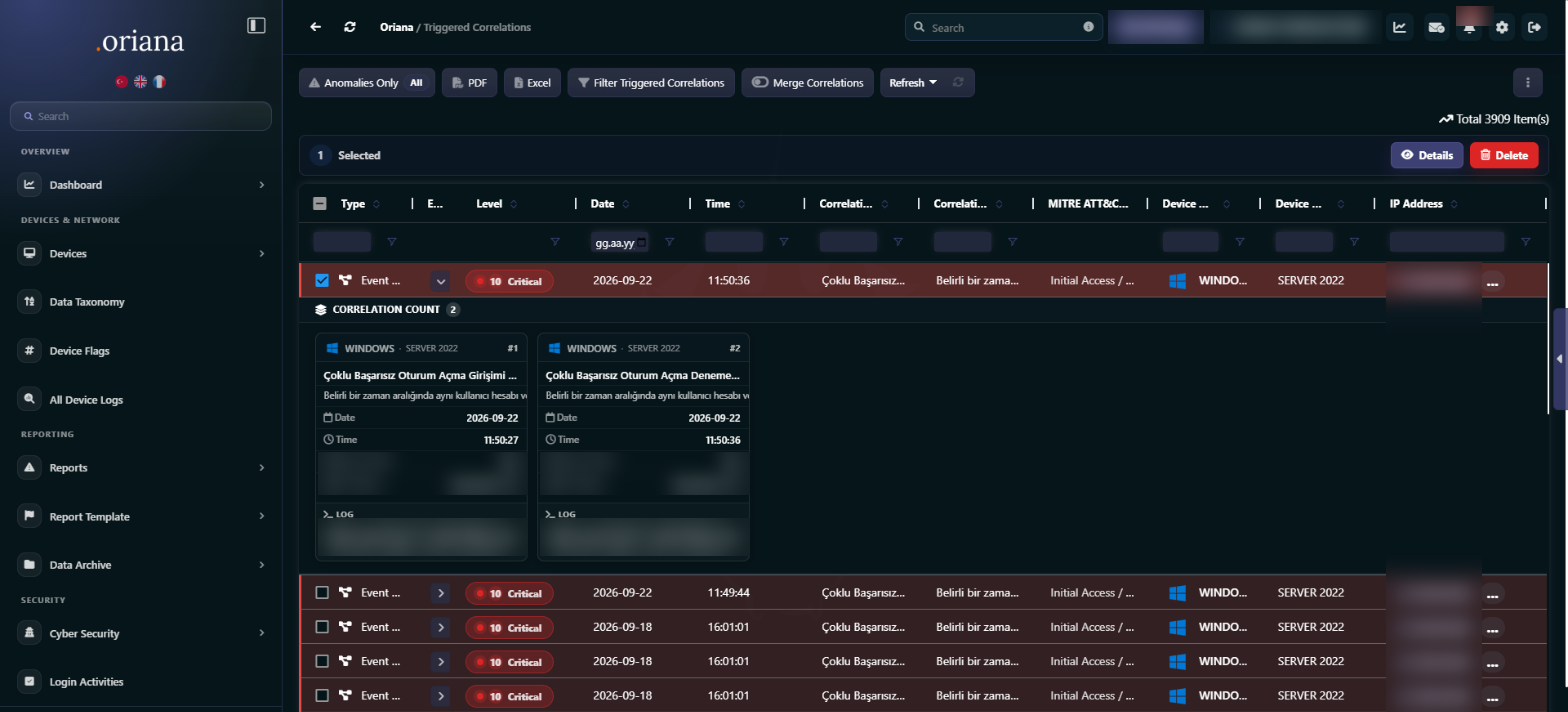
OrianaSIEM maps detected events to MITRE ATT&CK tactics and techniques so analysts understand faster which stage an attack has reached. USOM and CTI feeds are synchronized daily; access to a malicious link, address or phishing site raises an alarm instantly.
Threat Intelligence Feeds
IoC support for USOM, CERT-EU, CISA, NCSC, Abuse and Spamhaus. MITRE ATT&CK synchronization via STIX/TAXII.
Cyber Attack Shield
Detect traffic to or from thousands of known malicious IPs and URLs; make DoS/DDoS-driven activity visible.
Alarm Actions
E-mail (queue-based), SMS (multiple providers), automated SSH command on trigger; cooldown, hourly caps, alarm merging and grouping.
Event Tagging (1-10)
Every event is tagged with a severity level: 1-2 informational, 3-4 monitor, 5-6 may affect operations, 7-8 significant, 9-10 critical. Updated tags are pushed to the system regularly.
Key features of the SIEM solution
Every layer of the SIEM platform, from data collection to tenant management.
Data Collection and Connectivity
- Multi-source log support, vendor-agnostic
- Agent-based / agentless collection (Syslog UDP/TCP, Syslog TLS, Oriana Agent)
- NetFlow / sFlow and telemetry support
- SFTP, SMB, FTP file sources; log import
- Automatic device discovery
Data Security and Continuity
- Secure transport over TLS
- Buffering, retry mechanism, backpressure management
- Lossless processing under load with event queue and cache
- Log signing / hash verification
Parsing and Normalization
- Common data model, raw log retention
- CEF / LEEF / JSON / XML / Syslog support, multiline logs
- AI-assisted log parsing (for new sources)
- Field extractors, data taxonomy
- Time standardization, event ordering, duplicate detection
Enrichment and Context
- Source and access enrichment
- Cyber threat intelligence (IoC) enrichment
- GeoIP / IP information service integration
- MITRE ATT&CK tactic/technique tags
Search, Analysis and Threat Hunting
- Data warehouse search; search across all devices; pivot search
- Operators: equals, contains, greater/less than, between, AND/OR, regex, CIDR
- Filter shortcuts; saved and shareable queries
- Timeline view, right-click menu, IP information window
Dashboards and Reporting
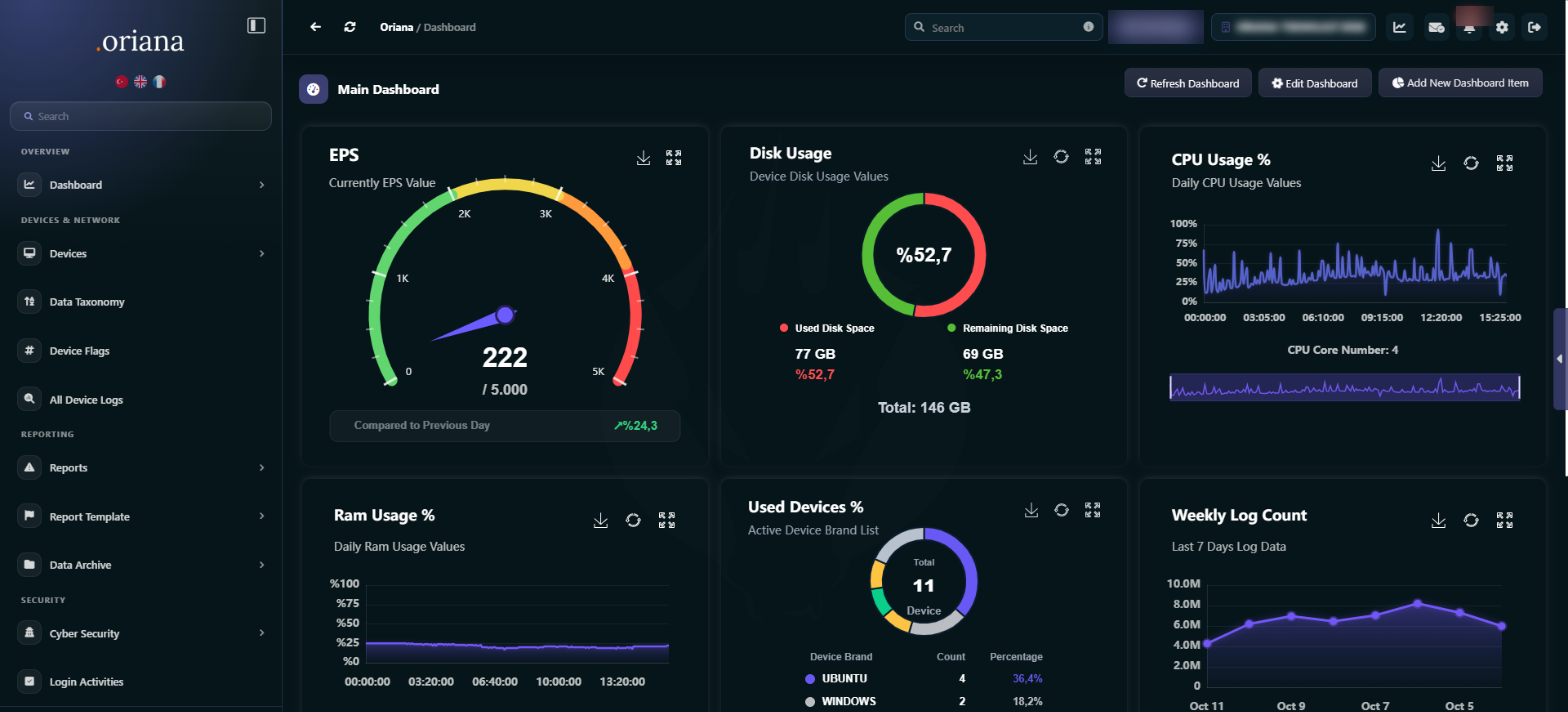
- Multi-page, multi-tab dynamic dashboards; auto-refresh
- EPS, CPU/RAM, device and license usage charts
- On-demand, daily, weekly, monthly reports; e-mail distribution
- Dynamic report designer, templates and report store
- PDF and Excel export; raw log reports
Alarm and Incident Management
- Alarm prioritization and merging
- Triggered correlation records, evidence and note attachment
- Automated actions: e-mail, SMS, SSH command
- Simulation mode, retry and error handling
Archive and Retention
- Daily automatic archive; per-device retention periods
- Legally valid time stamping under Turkish e-signature law 5070
- Create and download archives for custom date ranges
- Backup transfer to SFTP; configuration backup / restore
Security, Access and Tenants
- RBAC: page-, button-, action- and endpoint-level permissions
- Multi-tenant (MSSP) support; isolated data per tenant
- Login via LDAP / Active Directory, SSO, 2FA, OTP, SMS
- Sensitive data masking, encrypted storage, audit logs
- IP range restriction, captcha, step-up authentication
SIEM capability without changing your existing infrastructure.
Native integration with leading firewalls through the firewall analyzer feature; ready-made connectivity to directory services, e-mail and SMS providers.
All integrationsFirewalls
Identity, Notification and Intelligence
Log Sources
Not features; measurable outcomes.
| Metric | OrianaSIEM impact | How? |
|---|---|---|
| MTTD (time to detect) | Decreases | Earlier detection through fast queries and correlation; 3,500+ ready-made rules |
| MTTR (time to respond) | Decreases | Central visibility, event context, MITRE mapping and automated actions |
| Analyst productivity | Increases | Profiling-based UEBA; no proprietary query language to learn |
| Detection coverage | Increases | Connecting a source does not grow the license; every log reaches the SIEM |
| Operational resilience | Increases | On-premise / hybrid deployment, microservice architecture, manufacturer-direct continuity |
| Cyber risk & audit | Decreases | Fewer audit findings and lower compliance risk; board-level reporting |
Linux-based, containerized, horizontally scalable.
Deployed with Docker on Ubuntu Server 22.04/24.04 LTS. Starts on a single server; as EPS grows, the collector, correlation and data layers scale independently. With no indexing layer, it needs less CPU and RAM than peers at the same EPS.
EPS-based sizing table| Environment | CPU | RAM | Disk | Note |
|---|---|---|---|---|
| Minimum / POC | 8 cores | 16 GB | 500 GB SSD, LVM | Low-volume environments and POC |
| Up to 5,000 EPS | 16 cores | 32 GB | 1.5 – 3 TB SSD | Reference level, single server |
| 17,000 EPS (field reference) | 32 cores | 64 GB | 4 TB | ~2 years of log retention |
| 30,000 – 50,000 EPS | 80 – 128 vCPU | 256 – 512 GB | NVMe hot + archive | Multi-server, replica/sharded |
Catch the attack as it happens, not after the fact.
A 1-2 week POC on your own log sources; let's measure query time, resource consumption and MTTD/MTTR scenarios together.