A Türkiye-made SIEM: your data stays with you, performance you can measure.
OrianaSIEM is developed in Türkiye and holds the A-Level Conformity Certificate from TRTEST SIEM testing. Your logs remain under your control; ready-made reports for Turkish Law 5651, KVKK and Cybersecurity Law 7545 as well as GDPR, NIS2 and ISO 27001; low resource consumption with the patented Minimize algorithm; and direct support from the vendor.
Reading from outside Türkiye? This page explains the local positioning for the Turkish market. For international readers, the same platform is covered from a data sovereignty, NIS2 and DORA perspective on the Data Sovereignty SIEM page.
Choosing a domestic SIEM is not an emotional decision; it is a data, cost and continuity decision.
For public institutions, critical infrastructure and regulated industries, "where was the product built, where does the data live, who is accountable when something breaks" matter more than a feature list.
Data sovereignty
Logs stay in your own data center, in a hybrid setup or in the cloud of your choice. There is no need to ship critical logs to foreign data centers and no cloud egress cost, unlike foreign cloud SIEMs.
Ready for Turkish regulation
Two-year time-stamped, integrity-protected retention for Law 5651, KVKK access logs and breach detection, the BDDK Information Systems Regulation and the logging duties under Cybersecurity Law 7545, all with ready-made report templates.
Supply chain continuity
With foreign vendors, divestitures, licensing changes or sanctions can put a SIEM investment at risk. Oriana's roadmap, engineering team and support are in Türkiye; requests reach the product team directly.
Predictable total cost
Licensing is based on platform scope and retention period, without volume-based penalties. Connecting a new source does not inflate the license, so no log source is left outside the SIEM for cost reasons and detection coverage stays complete.
Direct vendor support
Interface in Turkish, English, German and French; SLA-backed resolution times, remote and on-site support, training. Parsers for new log sources are built by the vendor itself, so you never wait in an overseas support queue.
Independently verified maturity
The A-Level Conformity Certificate from TRTEST SIEM testing is an independent reference for the product's technical maturity, reliability and suitability for enterprise environments. Details on the About Us page.
Local and fast: a measurable difference from a patented architecture.
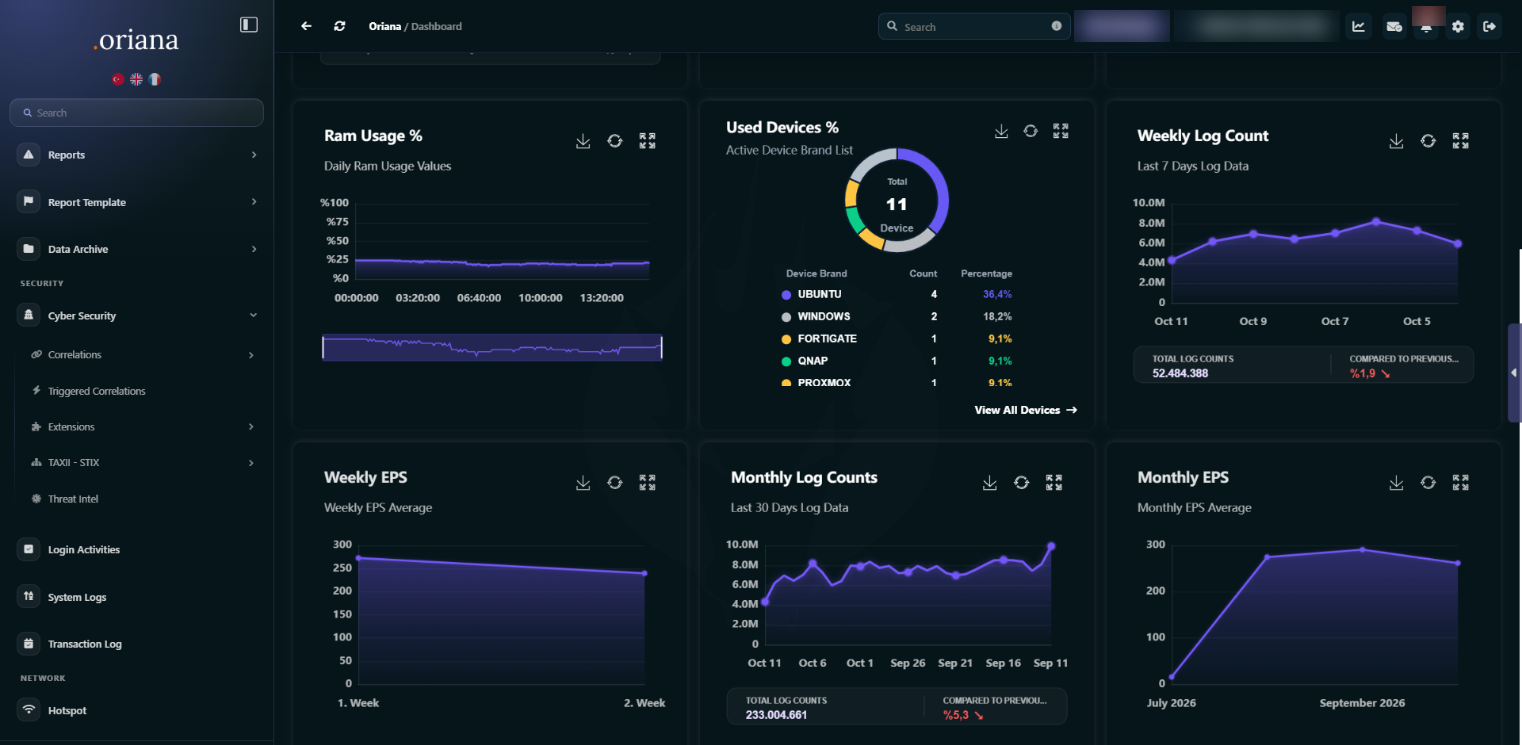
Domestic SIEMs are often chosen only because they are domestic. OrianaSIEM combines that advantage with performance: the patented Minimize algorithm and a proprietary data engine that is not based on Elasticsearch or the JVM deliver low resource consumption and fast queries at high log volumes.
The figures below were measured in internal test scenarios; the actual ratio in your environment depends on log types and is measured together during the POC.
Technical Specifications- MITRE ATT&CK mapping and STIX/TAXII synchronization
- USOM connector and daily-updated threat intelligence feeds
- Sigma and YARA rule support; no proprietary query language to learn
- Microservice architecture; zero-downtime updates with Docker/Kubernetes
Three approaches, the same questions.
The comparison is based on vendor documentation and market knowledge and shows decision factors rather than brand-by-brand claims. For a definitive answer we recommend a comparative POC on the same data set and the same hardware.
| Decision factor | Foreign cloud SIEM | Open-source deployment | OrianaSIEM (Türkiye-made) |
|---|---|---|---|
| Data location | Vendor cloud, usually a foreign data center | On-premises | On-premises, hybrid or the cloud of your choice; data sovereignty by design |
| License model | GB/day or GB/month ingest; cost grows with retention | License is free; operations are not | Based on platform scope and retention; no volume-based penalty |
| Queries and rules | Proprietary query language (KQL, SPL etc.) and certified experts | Cluster management, tuning and rule development stay with your team | UI-driven; 3,500+ ready-made rules, Sigma/YARA; no language learning curve |
| Resource consumption | Invisible to the customer, reflected in the price | High RAM and disk for Elasticsearch/JVM clusters | Significantly lower CPU/RAM in internal tests; up to 60% less disk |
| Turkish compliance reports | Global templates; no ready reports for 5651, KVKK, BDDK | Built by the customer | 5651, 5070, KVKK, BDDK, 7545 ready; GDPR, NIS2, ISO 27001, PCI DSS reports included |
| Accountability in audits | Foreign vendor, tiered support | No accountable vendor; community support | Direct vendor support with SLA, in Turkish and English |
| Time to value | Platform transformation; 6-12 months is common | Months of sizing and tuning | Installed in one day once the server is ready, a measured 1-2 week POC, live in days |
| UEBA | Usually a separately licensed module | Limited or a separate component | Profiling-based UEBA as standard; per user, IP, MAC, hostname |
| Continuity | Risk of acquisitions, divestitures and roadmap changes | Upgrade risk sits with your team | Product, R&D and support in Türkiye; vendor-managed updates |
Honest positioning. We say openly that global platforms lead in application ecosystem breadth and machine-learning-heavy advanced analytics. If data sovereignty, predictable cost, Turkish regulation, resource consumption, UEBA and direct vendor support are your priorities, OrianaSIEM is the better fit. We can test this with your own data.
Turkish regulations are part of the product design.
Whatever regulation applies to you, our goal is to cut audit preparation measured in person-days: ready report templates, time stamping and integrity mechanisms, and deduplication to keep long retention affordable. See the Regulatory Compliance page for international equivalents.
Access and traffic records retained for at least two years with time-stamped integrity; ready-made 5651 reports.
Correlation of personal-data access logs, breach detection scenarios, anomalous access detection with UEBA and reporting for the 72-hour notification.
Incident detection, central monitoring and log retention duties; alert and report flows aligned with USOM and SOME processes.
Central monitoring of banking sources, audit trail integrity and retention, incident management records.
A.8.15 logging and A.8.16 monitoring controls, PCI DSS Requirement 10, GDPR and NIS2 notification processes, reported from the same platform.
8 questions to ask before choosing a SIEM.
Ask these not only of us but of every SIEM vendor you evaluate. The answers become clear in a POC on your own data, not in a brochure.
Plan a Comparative POC- Three-year total cost calculated? License, hardware, storage, consulting and staff together.
- Sources left unconnected because of cost? Does adding a source grow the license?
- Where are critical logs stored? Is a foreign cloud compatible with your data policy?
- Proprietary query language required? How many experts do you have to write it?
- 5651, KVKK and BDDK reports ready out of the box? How many person-days does audit prep take?
- When the EPS limit is exceeded, what happens? Are events dropped or lost?
- Who will own the product in five years? Is there a written roadmap and support commitment?
- A POC on the same data measuring resource consumption, query time and deduplication ratio?
Migrate without falling into the "if it ain't broke" trap.
Run in parallel, measure, then switch, without turning off your current SIEM. Installation takes a day once the server is ready; the POC takes 1-2 weeks.
Discovery
Source list, daily log volume (GB/day, EPS), retention period, applicable regulations and success criteria are agreed together.
Installation
Installation is completed once the server or VM is ready; firewall, Active Directory, Linux and application sources are connected and parsers are validated.
Parallel measurement
Brute force, lateral movement, data exfiltration and privilege escalation scenarios; 5651 and KVKK reports; the same queries compared against your current product.
Phased migration
Sources are redirected in stages, historical records are imported and critical rules are rewritten with vendor support. The results report is board-ready.
Regulation, migration and gains.
A domestic SIEM is security information and event management software developed in Türkiye by a local vendor, with the engineering team, product roadmap and technical support located in Türkiye. Public institutions and critical infrastructure operators prefer it for data sovereignty, regulatory compliance and supply chain continuity.
Yes. OrianaSIEM is developed in-house by Oriana Teknoloji A.Ş., based in Teknopark Istanbul. The data engine and correlation infrastructure are Oriana's own; the product does not require Elasticsearch or Kibana. The only open-source components used are Redis and RabbitMQ.
OrianaSIEM earned the A-Level Conformity Certificate in SIEM testing carried out by TRTEST. The certificate is an independent assessment of the product's technical maturity and suitability for enterprise environments and can be used as a reference in public-sector and regulated procurements.
You decide: your own data center (on-premises), hybrid, Oriana cloud, a partner cloud or an appliance. With an on-premises deployment, data never leaves the country and there is no egress cost.
We recommend running in parallel with your current SIEM. Sources are first dual-sent to OrianaSIEM, historical records are imported, critical rules are rewritten with vendor support and the migration decision is made on comparative measurements. Installation takes a day once the server is ready; the POC takes 1-2 weeks.
Licensing is based on platform scope, retention period and use case, without volume-based penalties; EPS is used only for capacity planning. Monthly, annual and three-year subscription options are available. Contact us for a quote.
We state openly that global platforms lead in application ecosystem breadth and machine-learning-heavy advanced analytics. Profiling-based UEBA, more than 3,500 ready-made rules, the patented Minimize algorithm, low resource consumption and Turkish regulatory compliance are the differentiators you can measure in a POC.
Decide on measurement, not on a brochure.
Let us plan a 1-2 week comparative POC with your own log sources; installation takes one day.